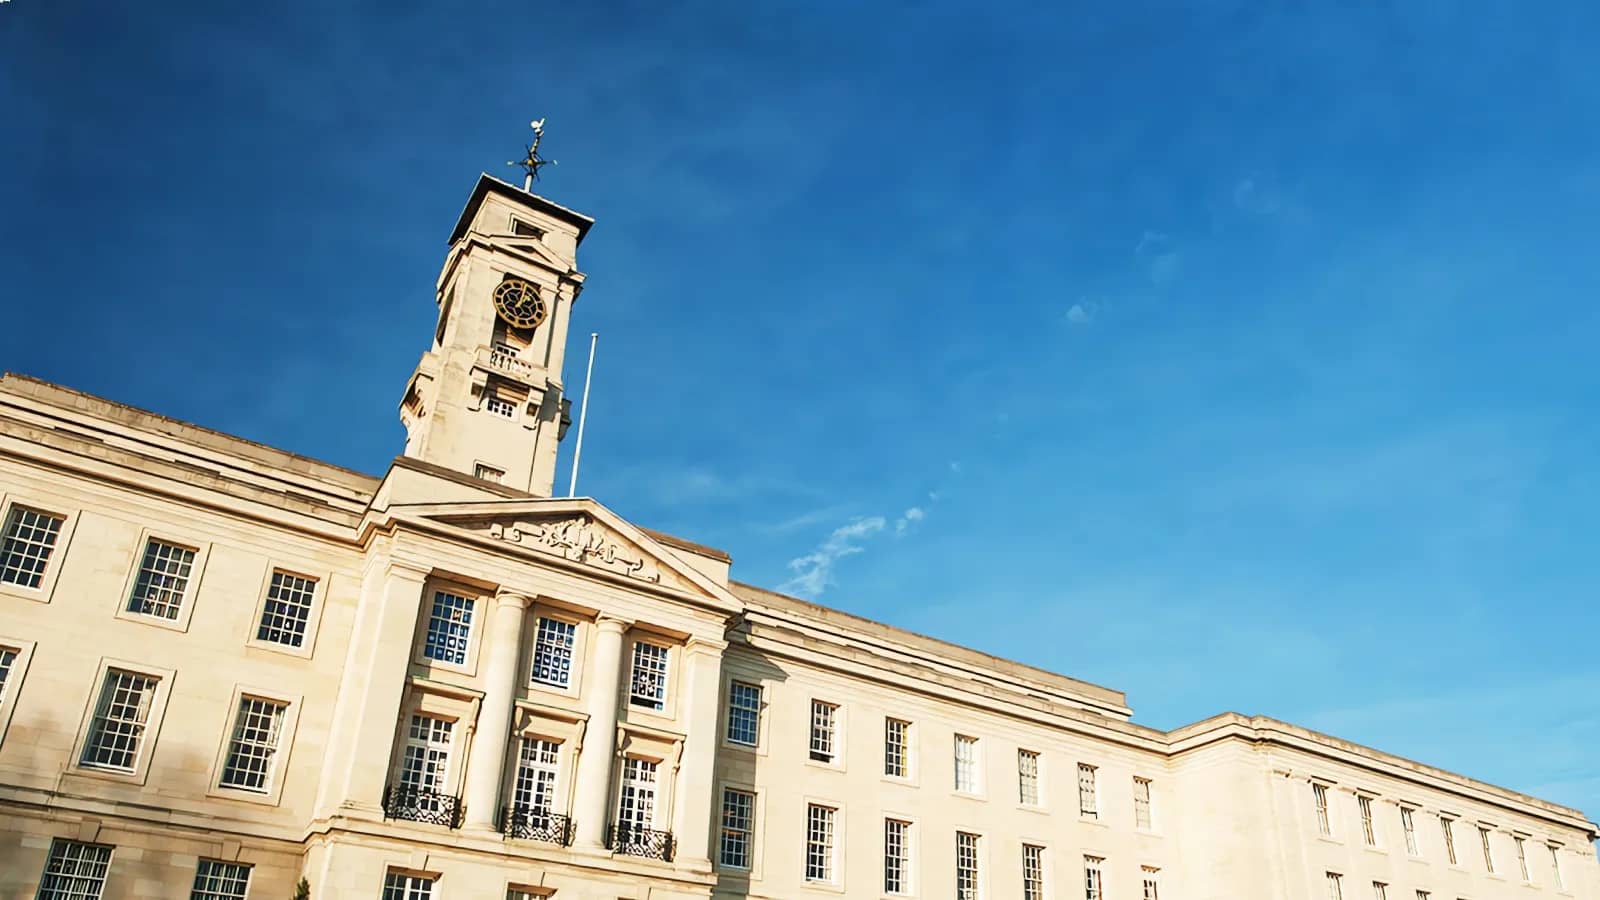
The University of Nottingham disclosed that attackers accessed its student records platform and exposed records for 454,600 current and former students. ShinyHunters asserted responsibility as part of an ongoing campaign that has hit over 100 organizations through Oracle PeopleSoft vulnerabilities.
The group has stolen data from over 100 organizations worldwide after breaching their cloud and on-premises Oracle PeopleSoft instances.
ShinyHunters told BleepingComputer that they are using a "gadget chain" of zero-days and old vulnerabilities in the attacks.
Universities remain prime targets for credential-stuffing and zero-day gadget chains against legacy PeopleSoft deployments; institutions should prioritize configuration hardening and third-party platform audits to limit lateral movement.
Tap a lens to see what this story means for you.
Liked this? The Brief brings you the whole day in tech, verified, every morning.
Two minutes, free forever. What's in The Brief →
See what’s happening right now
The Feed runs all day — short, verified briefs the moment they break.
Open the FeedFollow @thecircuitry_
Every story we publish, as it happens. No noise between.
Reader-supported
The Circuitry is a passion project I've always wanted to build, and I love the work behind it.
Running it costs real money. APIs, hosting, time. To keep improving the site and growing this into something useful for everyone, those costs have to be covered.
Any contribution is appreciated. If not, no pressure. Thanks for reading.
ShinyHunters published data from 12.9 million genuine Carhartt accounts after the apparel company refused a $3.3 million ransom. The breach, which also exposed records for more than 15,000 employees, originated from Carhartt's Databricks analytics platform.
ShinyHunters obtained and later leaked personal data belonging to 1.6 million RingCentral accounts after a July breach. The incident touched only a limited portion of the cloud communications provider’s customers and left core services untouched.
Mathspace disclosed that attackers stole personal data belonging to 1,079,819 students, staff, and parents or guardians in Australia and New Zealand after breaching its Metabase system. The incident is the latest in a campaign exploiting a Metabase zero-day vulnerability used by multiple companies.
The FBI is investigating the dark web sale of scans from more than 153 million US and Canadian drivers licenses obtained via an ongoing breach at a Louisiana identity verification company. The incident underscores the lasting danger of stolen physical identity documents that cannot be reset like passwords and the growing scale of cyber-enabled identity theft.
Capcom says about 11.77 million CAPCOM ID records were exposed, each with an email address and login metadata. 43 also exposed birth date, gender, country and nickname, and 196 accounts had passwords changed without authorization and reset. Capcom says it has not confirmed any compromise of customer-set passwords, and credit card information was not included.