
News
Every story we’ve published. Sourced, cross-checked, fact-verified.
Primary-source scoops, checked before they ship. What's in The Brief →
Linux Kernel 7.3 Released with Record 18,765 Commits
Linus Torvalds released Linux kernel 7.3 with a record 18,765 non-merge commits from 3,021 developers. The update adds features including sched_ext completion, failfs, and fchroot() while the 7.4 merge window opens next.
DigiTimes: Blackstone receives Anthropic proposal for over 10 percent yield on 60 billion dollar chip funding
DigiTimes: Anthropic has proposed to Blackstone a financing structure promising returns above 10 percent to back a 60 billion dollar package for Google tensor processing units totaling around 1.5 gigawatts, internally labeled Project North Star, amid higher infrastructure costs.
This week in crypto: Richard Heart detained, Ledger Atom, Starknet's post-quantum vote
Richard Heart's detention in Istanbul preceded a roughly $246 million drop in HEX's market cap, Ledger unveiled its $849 Atom wallet, and Starknet put a post-quantum layer-1 move to a vote, per Cointelegraph's weekly digest.
Tesla-SpaceX Merger Talk Builds Ahead of Tesla's Oct. 21 Earnings Call
Seeking Alpha asked its analysts whether Tesla should merge with SpaceX after Barclays said an all-stock deal could be announced before Tesla's annual meeting, expected by Dec. 6. No merger has been announced. Musk's "more and more overlap" remark came on Tesla's July 22 call; the next one is Oct. 21.
CISA adds two actively exploited AhsayCBS flaws to KEV catalog
CISA added AhsayCBS flaws CVE-2026-105134 and CVE-2026-105133 to its Known Exploited Vulnerabilities catalog on October 14, with an October 17 deadline for federal agencies. Attackers are chaining them to plant webshells and cryptominers, and Ahsay says its first patches did not fully fix them.
Apple Expands App Store Rules to Block AI Deepfakes
Apple has expanded its App Store rules to require developers to proactively prevent and remove AI-generated deepfakes and nonconsensual intimate imagery. The changes also target hidden nudify features and extend existing bans to alternative app distribution.
BeyondTrust Remote Support Zero-Day CVE-2026-102764 Hit in August, Now on CISA KEV
BeyondTrust Remote Support through 26.2.3 has a critical origin-validation flaw (CVE-2026-102764, CVSS 4.0 9.3) that attackers exploited as a zero-day on Aug. 29. CISA added it to KEV on Oct. 16 with an Oct. 19 deadline; self-hosted customers need the BT26-05-RS patch.
bbs-go Through 4.4.6 Vulnerable to Google One Tap Account Takeover (CVE-2026-111639)
bbs-go through 4.4.6 has a Google One Tap login flaw (CVE-2026-111639) that skips ID-token audience checks, letting attackers replay tokens from any OAuth client to take over Google-linked accounts. VulnCheck rates it 8.1 (CVSS 3.1) and 8.6 (CVSS 4.0).
CISA Adds Actively Exploited Fortinet CLI Flaw CVE-2025-61624 to KEV
CISA added Fortinet CLI path traversal flaw CVE-2025-61624 to its Known Exploited Vulnerabilities catalog with an Oct. 19 deadline. It lets an admin with read-write rights write or delete files on FortiOS, FortiProxy, FortiPAM and FortiSwitchManager; fixed releases cover current branches.
Steam Beta Adds Achievement Sets to Isolate DLC Progress
Steam's client beta adds Achievement Sets so developers can group base-game, DLC, and seasonal achievements without resetting existing completion. The redesigned achievements page adds friend comparison and filters, and 17 titles support the feature in beta.
FreeRDP 3.29.0 before 3.32.0 hit by CVE-2026-111380 heap overflow
FreeRDP versions 3.29.0 before 3.32.0 contain an integer overflow in the Apple audin backends (CVE-2026-111380) that leads to a heap out-of-bounds write. VulnCheck as the CNA rates the flaw 8.8 under CVSS 3.1 and 8.7 under CVSS 4.0.
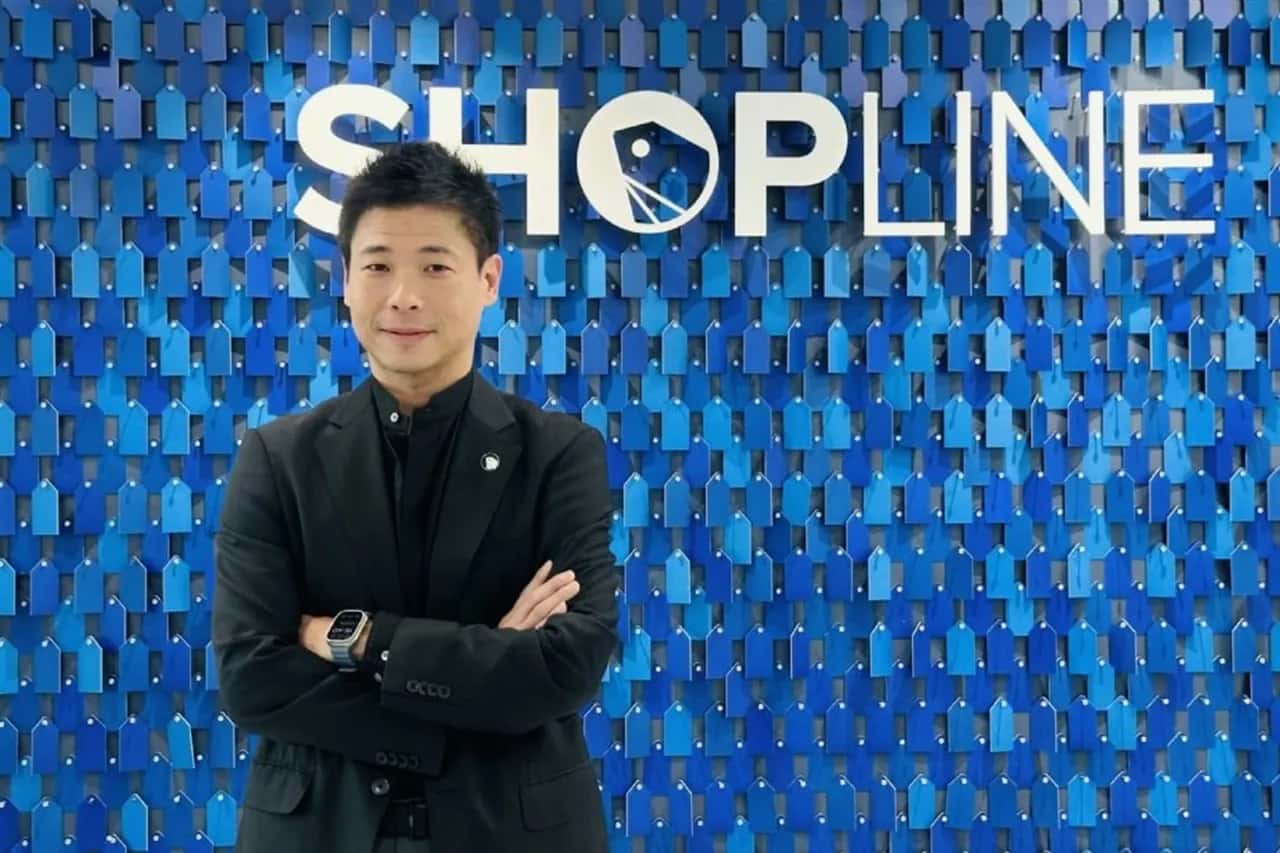
Shopline GMV Reportedly Grows 20% in 2026, DigiTimes Says
DigiTimes reports Shopline said its overall GMV rose 20% in 2026 compared with 2025, linking the result to a broader shift toward AI-assisted shopping and intelligent operations.
Lenovo Baiying PC Client vulnerable to privilege escalation flaw
Lenovo disclosed CVE-2026-92629, a high-severity improper authorization flaw in Baiying PC Client versions before 1.1.0.295 that could allow local authenticated users to execute arbitrary code with elevated privileges. Lenovo PSIRT as the CNA rates the issue 7.3 under CVSS 3.1 and 7.0 under CVSS 4.0.
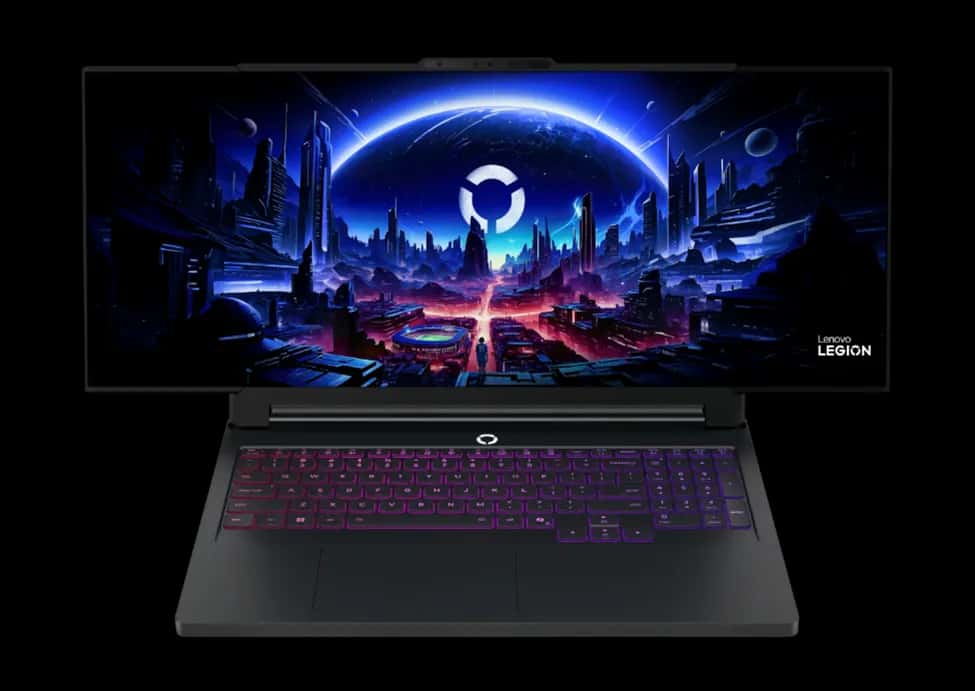
Lenovo fixes high-severity flaw in Legion Zone app before 2.0.28.8182
Lenovo has fixed CVE-2026-75941 in the Legion Zone application before version 2.0.28.8182. Lenovo PSIRT as CNA rates the flaw 8.0 under CVSS 3.1 and 8.6 under CVSS 4.0, allowing same-network arbitrary code execution in the China-only app.
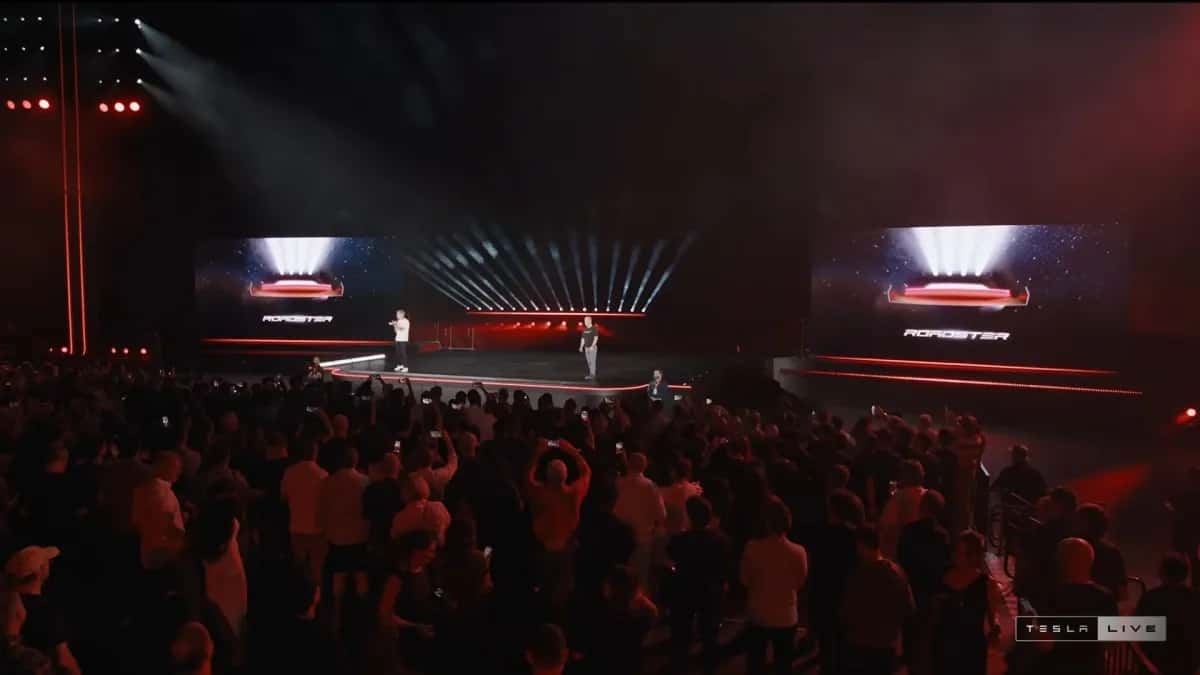
Tesla Unveils Its Next-Gen Roadster: Everything Announced
Tesla unveiled its next-gen Roadster in three configurations, including a one-seat Rocket version that can fly. Tesla lists more than 300 miles of range, more than 230 mph and 0–60 in under 0.59 seconds for the Rocket. Deposits are $50,000 (Performance) and $250,000 (Thrust); Rocket is invite-only. Final prices aren't announced, and production starts in 2028.
ASML Patents Signal Hybrid Bonder for Advanced Packaging
Patent filings analyzed by SemiAnalysis show ASML developing a die-to-wafer hybrid bonder for advanced packaging. The move positions the lithography leader against Besi and other suppliers as chipmakers seek growth beyond transistor scaling.
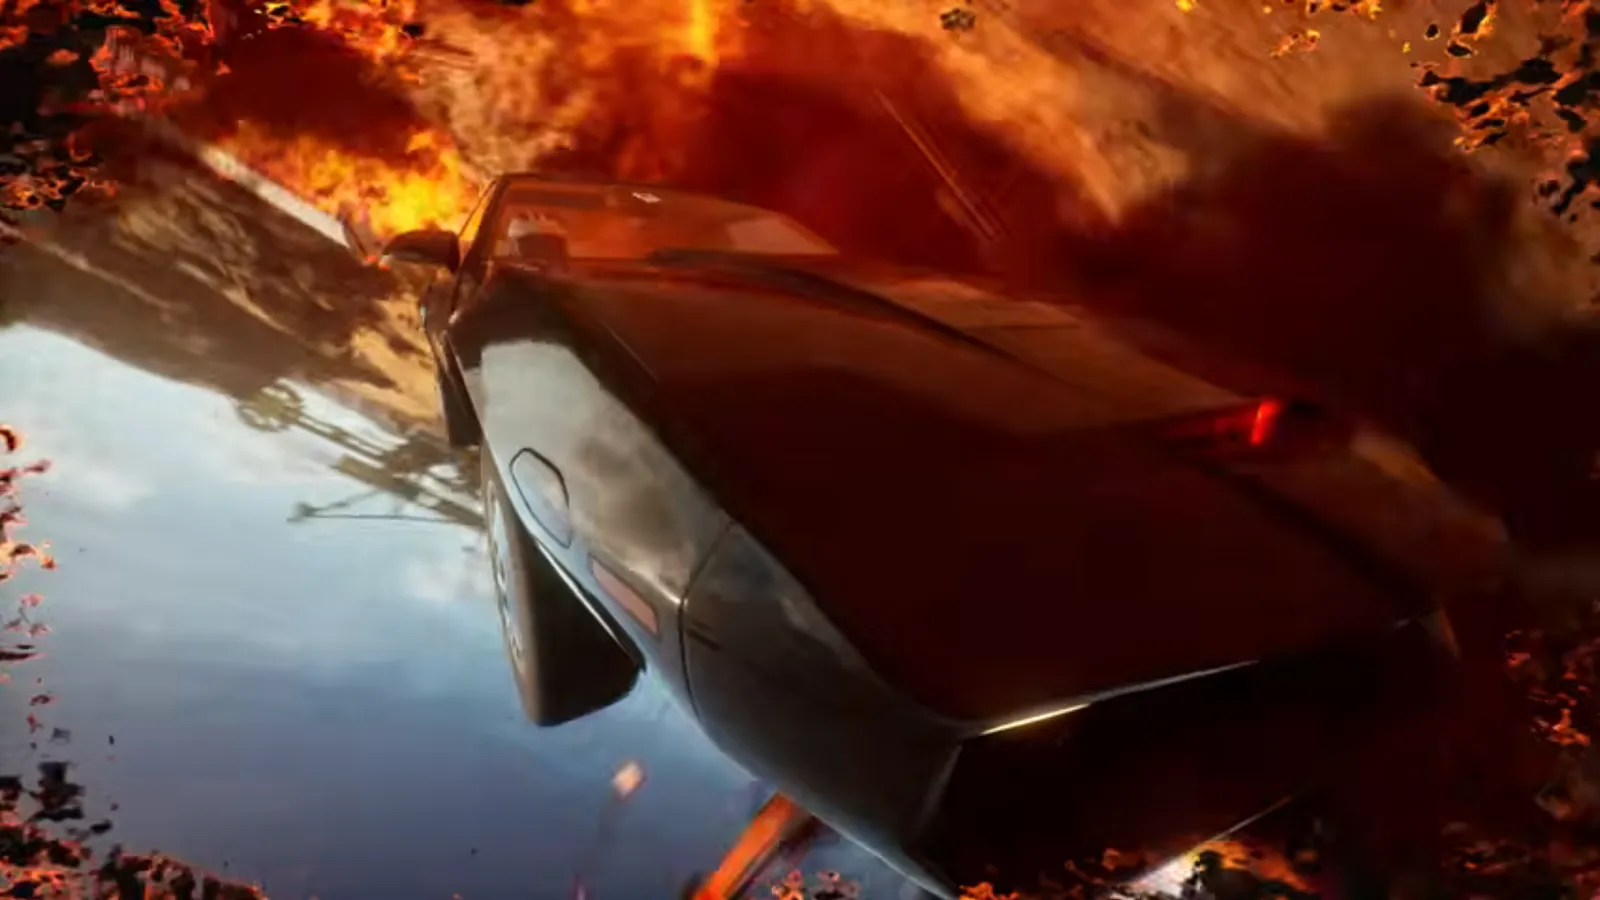
Stuntman: Hollywood Shows Knight Rider K.I.T.T. Gameplay
A gameplay trailer for Stuntman: Hollywood debuted on October 15 and features Knight Rider's K.I.T.T. The single-player stunt game is available to wishlist on PS5, Xbox Series X|S, and PC.
DigiTimes: ByteDance in advanced talks with MediaTek for custom data center chips
DigiTimes: ByteDance is in advanced talks with MediaTek to buy custom data center chips, and an agreement could come soon, according to people familiar with the matter. Bloomberg first reported the talks, saying a deal would help MediaTek compete with Qualcomm and Broadcom in data centers.
Microsoft SharePoint Server Subscription Edition hit by CVE-2026-108452
Microsoft disclosed CVE-2026-108452, an 8.8 path traversal RCE in SharePoint Server Subscription Edition before 16.0.20326.20190. KB5002927 fixes it; an authenticated Site Owner can exploit it over the network.
Microsoft discloses high-severity ASP.NET Core DoS flaw CVE-2026-109468
Microsoft disclosed CVE-2026-109468, a 7.5 ASP.NET Core denial-of-service flaw affecting Visual Studio 2022 before 17.14.42, Visual Studio 2026 before 18.10.4, and System.Formats.Cbor before 10.0.13.
Tech roundup: iPhone Duo repairs, OpenAI claims, Safari push
October 15 tech stories on 9to5Mac Daily include iPhone Duo repair pricing, OpenAI allegations involving a former employee now at Apple, Apple's Safari campaign, and a reported Apple Intelligence timeline for China.
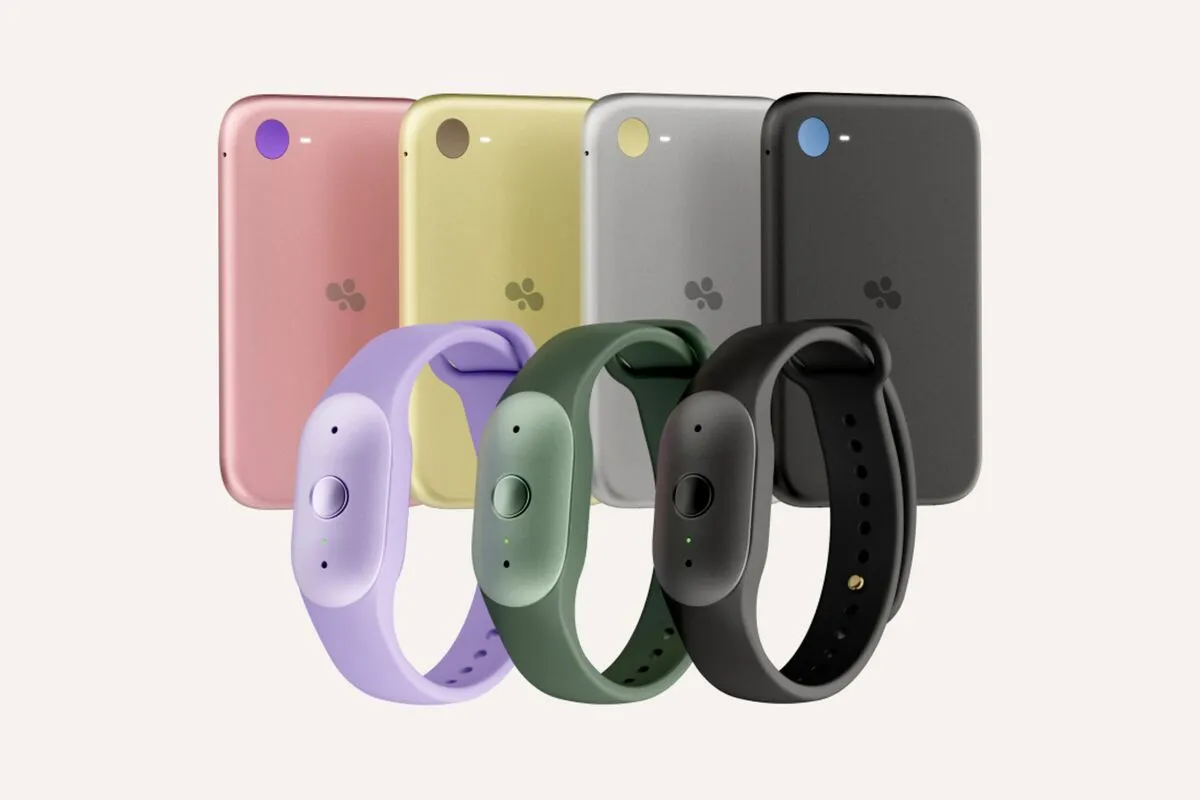
Amazon Announces $74.99 Bee Frontier AI Wearable
Amazon's Bee unit launched the $74.99 Bee Frontier AI wristband, available now in the US, and announced the Bee Eclipse phone attachment, starting at $99.99 and coming soon.
Renovatebot Renovate hit by high-severity SSRF flaw CVE-2026-110868
Renovate before 44.79.0 and five Mend Renovate products have a high-severity SSRF flaw, CVE-2026-110868, that can expose cloud credentials. VulnCheck rates it 8.5 under CVSS 3.1.
CISA Adds Atlassian Multi-Product File Access Flaw to KEV Catalog
CISA has included CVE-2026-21589 in its known exploited list, covering eight Atlassian Data Center products with a short compliance window.