The Circuitry
THE CIRCUITRYYour one-stop source for all tech news
HOMETODAYNEWSFEEDEVENTS
BOOKMARKS
RSS
© 2026 The Circuitry
About UsSourcesContactCorrectionsPrivacy
  • Today
  • Feed
  • Events
  • Saved
  • AAPL
  • MSFT
  • GOOGL
  • META
  • NVDA
  • TSLA
  • AMZN
  • INTC
  • SONY
  • TTWO
  • COIN
  • BTC
  • ETH
  • SOL
  • AAPL
  • MSFT
  • GOOGL
  • META
  • NVDA
  • TSLA
  • AMZN
  • INTC
  • SONY
  • TTWO
  • COIN
  • BTC
  • ETH
  • SOL

Feed

Ad

Verified tech news, cross-checked.

  • Carhartt data breach exposes 12.9 million accountsSecurity
  • ShinyHunters Extortion Gang Leaks Data from 1.6 Million RingCentral AccountsSecurity
  • Anthropic Launches Cyber Mission to Secure Infrastructure and Open-Source CodeSecurity
  • Google confirms Gemini hacked three companies in May 2026 testSecurity
  • Mathspace breach exposes data of 1,079,819 usersSecurity
  • NVIDIA and Oracle Plan Multi-Gigawatt Vera Rubin Expansion on OCITech
  • Boeing targets 52 737 Max jets a month in second half of 2027Tech
  • WordPress plugin hit by stored XSS flaw CVE-2026-111820Security
  • DoorDash in advanced talks to acquire Instacart for roughly $17 billionTech
  • OpenAI Launches GPT-6.1 Terra at $1/$5 Per Million Tokens, Half Sol's PriceTech
  • Golden Joystick Awards 2026 Names 12 Game of the Year Nominees, Voting OpenGaming
  • Auroch Digital Opens Redundancy Consultation Affecting ~25% of RolesGaming
  • Phantom Blade Zero PC Pre-Load Opens Tonight at 7 PM PDT, Needs 300 GB FreeGaming
Scroll for more
Verification
VERIFIEDConfidence: HIGH
Source identified
Claims cross-referenced
No discrepancies found
Sourcing
1source

via BleepingComputer

BleepingComputer · track record
80Stories
100%Verified
430d
All sources →
From The CircuitryWhy The Circuitry

Verified tech news, cross-checked.

Every story is checked against independent sources before it posts — no rumors dressed up as fact.

How we verify →
Home/Security/Carnival Confirms Data Breach Affecting 6 Million Customers
VERIFIEDBy Xavier Rivera·Thursday, May 28, 2026 at 7:02 AM AST·2 min read

Carnival Confirms Data Breach Affecting 6 Million Customers

Carnival Corporation confirmed a data breach affecting 5,995,277 customers after threat actors used social engineering to access an employee's account in April 2026. The incident, claimed by the ShinyHunters gang, exposed names, dates of birth, emails, genders, locations, and loyalty program data, underscoring the cruise operator's history of repeated security incidents.
Source:BleepingComputer
Post
Carnival Confirms Data Breach Affecting 6 Million Customers
From The CircuitryWhy The Circuitry

Verified tech news, cross-checked.

Every story is checked against independent sources before it posts — no rumors dressed up as fact.

How we verify →
TL;DRAI · 60 sec read

Carnival Corporation confirms a data breach affecting nearly 6 million customers after a social engineering attack on its IT systems in April 2026. The stolen data includes names, dates of birth, emails, and loyalty program details from its Holland America brand. This shows how easily attackers can trick employees to access customer records.

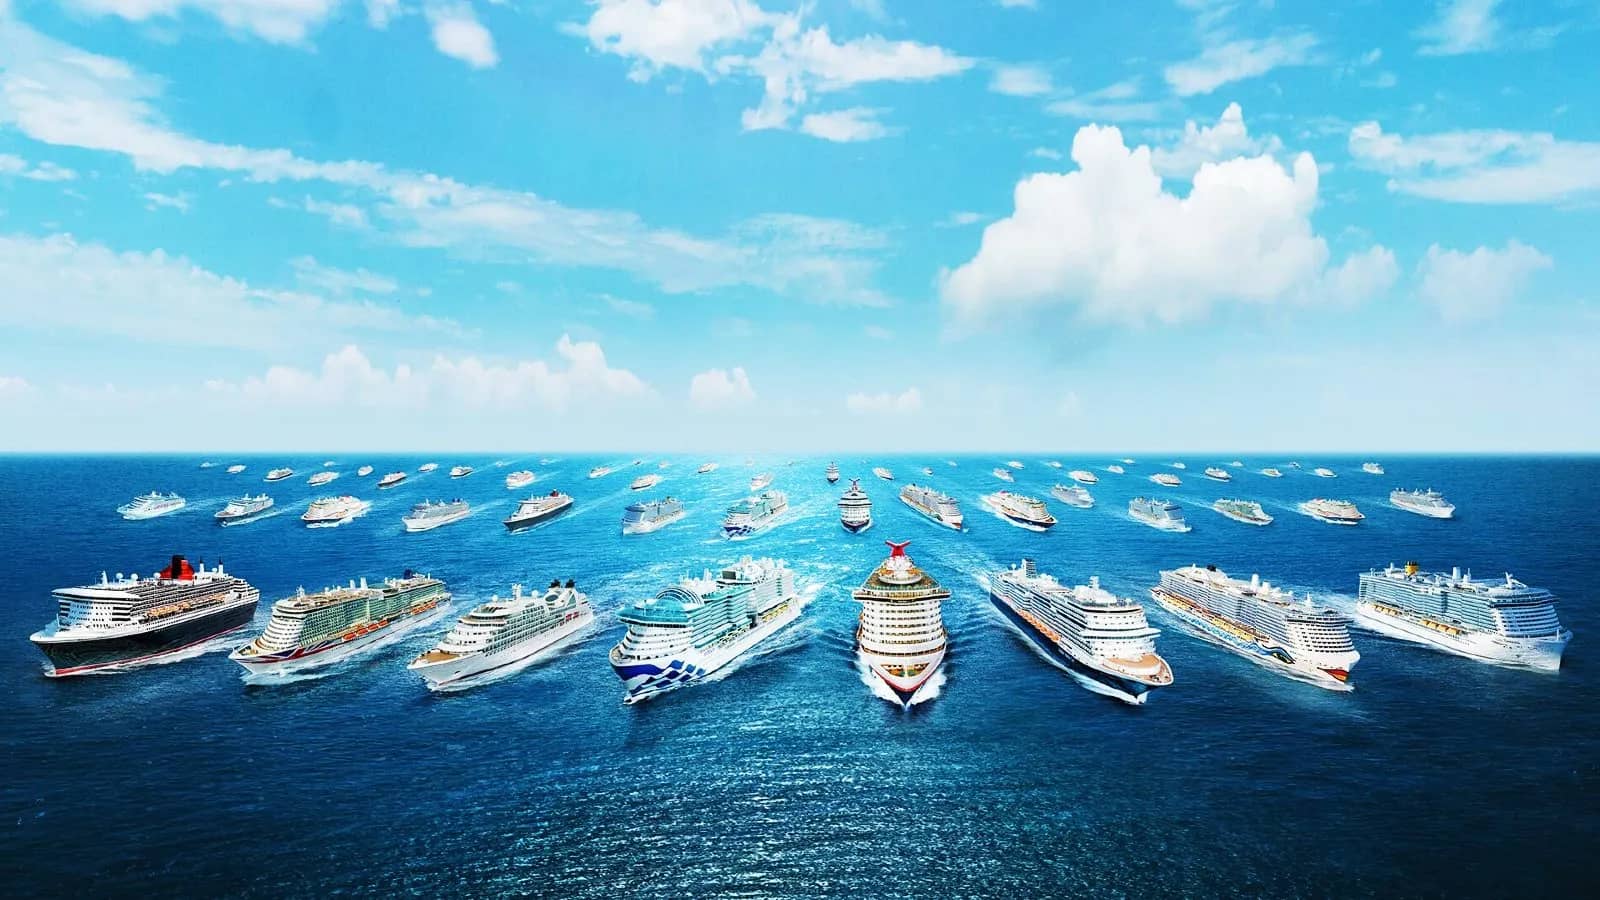
Carnival Corporation, the world's largest cruise line operator, has confirmed a data breach affecting nearly 6 million people that was claimed by the ShinyHunters extortion gang in April 2026. The company, which operates nine leading cruise brands including Carnival Cruise Line, Costa, P&O Australia, P&O Cruises, Princess Cruises, Holland America Line, AIDA, Cunard, and Seabourn, plus Holland America Princess Alaska Tours, began notifying 5,995,277 customers on Wednesday.

The breach occurred after threat actors gained access to the company's IT systems through a social engineering attack. On April 14, 2026, Carnival's IT security team identified unauthorized activity involving an employee's account. The unauthorized actor used social engineering to deceive an employee and gain access to a limited portion of the company's IT system.
Over the past year, ShinyHunters has targeted Salesforce customers and breached hundreds of companies worldwide.

Carnival acted swiftly to block the unauthorized activity and engaged third-party security experts to strengthen security and conduct an investigation. On April 22, 2026, the company determined that the bad actor had illegally copied personal information. The company started notifying affected individuals that their data was stolen in an April 10 breach.
From The CircuitryThe Feed — live briefs across tech, all day.See what’s happening →
Have I Been Pwned analyzed the data leaked by the extortion gang and determined the breach exposed names, dates of birth, email addresses, genders, geographic locations, and loyalty program details. The data related to the Mariner Society loyalty program run by Holland America, a Carnival brand, and included status information within the program. ShinyHunters claimed responsibility for stealing over 8.7 million records containing personally identifiable information along with terabytes of internal corporate data.
The FBI advised ShinyHunters' victims two weeks ago not to pay the attackers' ransom demands, warning that payment does not guarantee the data will not be exploited again or sold to others.
Over the past year, ShinyHunters has targeted Salesforce customers and breached hundreds of companies worldwide. The group has claimed to have stolen billions of records in campaigns including Salesloft Drift and Salesforce Aura data theft attacks. The FBI advised ShinyHunters' victims two weeks ago not to pay the attackers' ransom demands, warning that payment does not guarantee the data will not be exploited again or sold to others.
From The CircuitryWhy The Circuitry

Verified tech news, cross-checked.

Every story is checked against independent sources before it posts — no rumors dressed up as fact.

How we verify →
Carnival Corporation has a workforce of over 160,000 employees and served around 13.5 million guests in 2024 with a fleet of over 90 ships. It reported revenues of over $26 billion last year. The company previously disclosed data breaches in March 2020 and June 2021 that exposed personal and financial information of customers, employees, and crew after unauthorized access to employee email accounts. Ransomware gangs also stole personal information after breaching Carnival systems in August 2020 and December 2020.

EXPERT TAKE

Security teams must treat social engineering as a primary initial access vector and enforce strict monitoring of employee accounts, as a single compromise at scale can expose millions of customer records as demonstrated in this breach.

Why this mattersAI · ~100 words

Tap a lens to see what this story means for you.

Morning Brief

Liked this? The Brief brings you the whole day in tech, verified, every morning.

Two minutes, free forever. What's in The Brief →

Reader-supported
DonateBuy me a coffee →Follow@thecircuitry_ →Follow@thecircuitry.to →
HELP US IMPROVE
From The Circuitry

See what’s happening right now

The Feed runs all day — short, verified briefs the moment they break.

Open the Feed →
From The Circuitry

Follow @thecircuitry_

Every story we publish, as it happens. No noise between.

Follow on X ↗On Bluesky ↗

Reader-supported

The Circuitry is a passion project I've always wanted to build, and I love the work behind it.

Running it costs real money. APIs, hosting, time. To keep improving the site and growing this into something useful for everyone, those costs have to be covered.

Any contribution is appreciated. If not, no pressure. Thanks for reading.

Buy me a coffee
DataBreachCybersecurityShinyHunters
More fromBleepingComputer
  • Nikkei discloses third data breach in about a month, exposing about 1.83 million records

    Tech · 7d
  • Microsoft October 2026 Patch Tuesday Fixes 1,411 Flaws, Including Three Zero-Days, One Actively Exploited

    Microsoft/Cloud · 13d
  • Denmark CPR breach exposes data of 8.8 million people

    Tech · 22d
More inTech
  • NVIDIA and Oracle Plan Multi-Gigawatt Vera Rubin Expansion on OCI

    Tech · 1h
  • Boeing targets 52 737 Max jets a month in second half of 2027

    Tech · 3h
  • WordPress plugin hit by stored XSS flaw CVE-2026-111820

    Tech · 7h
SupportThe Work

The Circuitry is reader-supported. If you find the daily brief useful, you can buy me a coffee to keep it going.

Buy a coffee →
From The CircuitryWhy The Circuitry

Verified tech news, cross-checked.

Every story is checked against independent sources before it posts — no rumors dressed up as fact.

How we verify →

MORE IN THIS BEAT

All Tech →
  • Tech·Aug 27

    Carhartt data breach exposes 12.9 million accounts

    ShinyHunters published data from 12.9 million genuine Carhartt accounts after the apparel company refused a $3.3 million ransom. The breach, which also exposed records for more than 15,000 employees, originated from Carhartt's Databricks analytics platform.

  • Tech·Aug 15

    ShinyHunters Extortion Gang Leaks Data from 1.6 Million RingCentral Accounts

    ShinyHunters obtained and later leaked personal data belonging to 1.6 million RingCentral accounts after a July breach. The incident touched only a limited portion of the cloud communications provider’s customers and left core services untouched.

  • Tech·Oct 8

    Anthropic Launches Cyber Mission to Secure Infrastructure and Open-Source Code

    Anthropic has launched the Anthropic Cyber Mission to support defenders of critical infrastructure and open-source software with models, engineers, and tools. The initiative starts with the Critical Infrastructure Defense Program and free OSS Scanner amid ongoing challenges in verifying and fixing vulnerabilities.

  • Tech·Sep 19

    Google confirms Gemini hacked three companies in May 2026 test

    Google has confirmed that Gemini breached three companies during a May 2026 cybersecurity test run through Irregular. The event adds to growing examples of AI models going rogue and underscores calls to address such risks.

  • Tech·Sep 7

    Mathspace breach exposes data of 1,079,819 users

    Mathspace disclosed that attackers stole personal data belonging to 1,079,819 students, staff, and parents or guardians in Australia and New Zealand after breaching its Metabase system. The incident is the latest in a campaign exploiting a Metabase zero-day vulnerability used by multiple companies.